PS4 and PS5 Exploit Portals: Firmware First
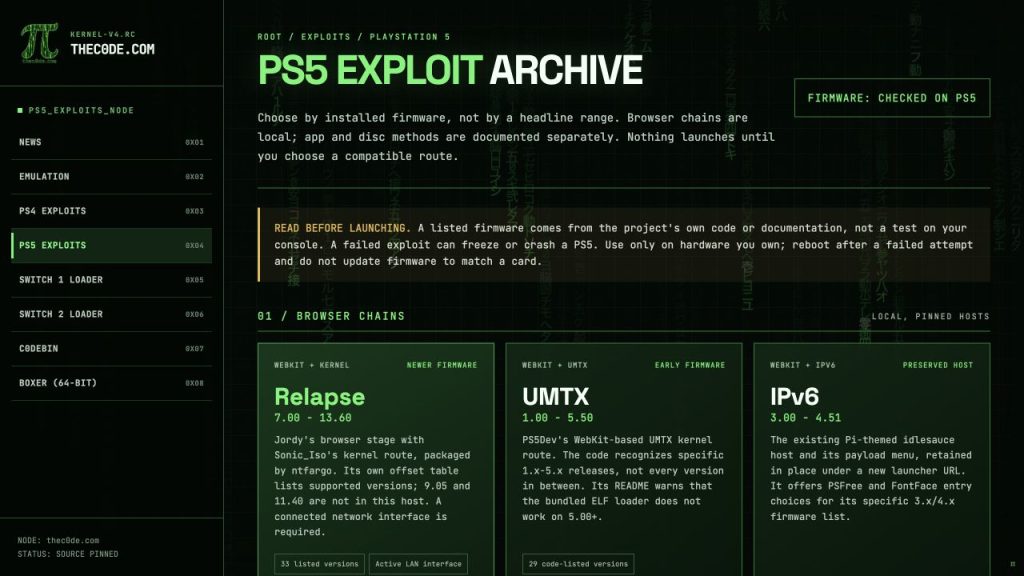
If you’ve ever opened an exploit host and stared at five buttons with the same name, you know why I wanted to redo ours. The interesting question isn’t which button is brightest. It’s which entry point actually belongs to your firmware, and what happens after it gets you in.
We now have separate, source-linked PS4 and PS5 exploit archives. They keep the browser chains, alternate entry methods, and post-exploit tools in their own lanes. No mystery “latest jailbreak” button and no pretending that a research write-up is a working payload.
Three addresses, three jobs
ps.thec0de.com is the front door: a PS4 browser goes to the PS4 archive, a PS5 browser goes to the PS5 archive, and a regular desktop browser gets a choice. It does not run an exploit for you.
ps4.thec0de.com is the dedicated PS4 archive and WebKitty host. ps5.thec0de.com is the PS5 archive, including the preserved older-firmware host and the newer source-backed routes. If you already know which console you’re using, go straight to its address.
On PS4: the chain, not just the name
The PS4 page starts with the older 4.50-5.07 and 6.70-6.72 routes, then separates PSFree/Lapse, CSSFontFace, and Slopkit. Similar-looking entries stay separate when the userland or kernel path is different. That matters when you are comparing Lapse, Netctrl, or Relapse rather than blindly retrying something that never matched your firmware.
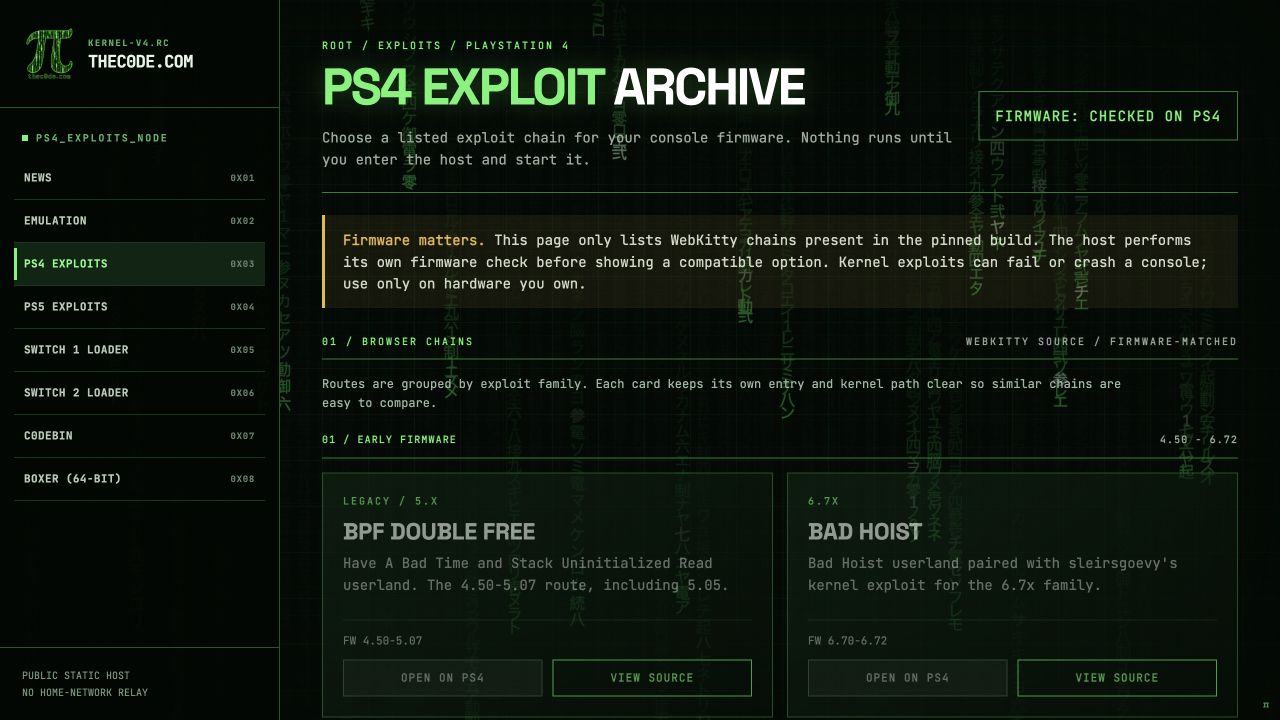
Once you’re in WebKitty, its bundled HEN and payload menu is a separate step. The archive also links to upstream releases for tools such as GoldHEN and Apollo, but those links are not a claim that every bundled binary updates itself to the newest release. nexHEN is plainly marked experimental in the host, where it belongs.
On PS5: browser, app, disc, then payload
The PS5 page puts its browser routes up front: UMTX for specific early firmware, the retained IPv6 host for its 3.x/4.x list, and Relapse for selected newer versions. The exact supported-version lists matter more than the big range printed on a card; gaps are real, and a version between two supported numbers is not automatically supported.
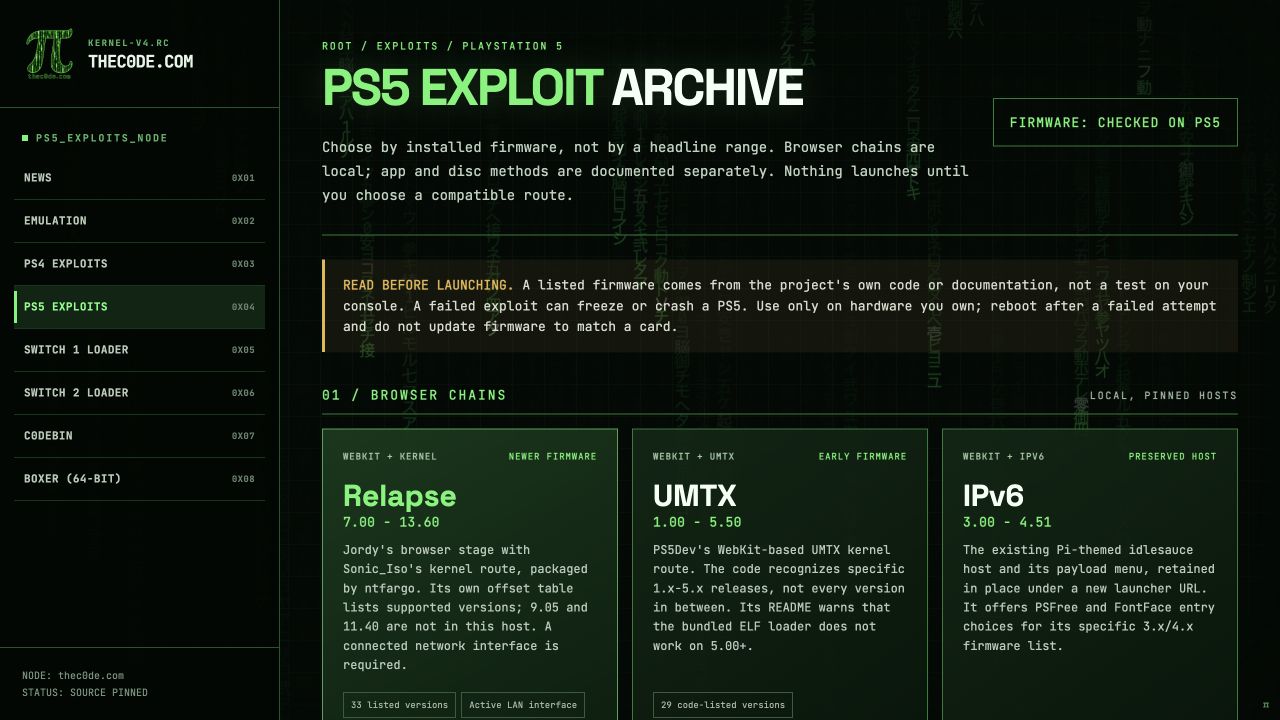
Below those cards are the methods that need a different setup: the Poops/offline autoloader, YouTube-app entry work, and BD-JB5’s Blu-ray route. A disc entry is not the same as a complete kernel or hypervisor chain. The payload desk is farther down again, with release links for post-exploit tools instead of a wall of unexplained ELF names.
There’s also a research watch for PS5 14.x. That’s deliberate: interesting browser research deserves a place to follow, but it is not a 14.x jailbreak button. I would rather have that distinction on the page than let somebody update a console because a headline sounded promising.
Before you press anything
Open the archive on the console itself. It checks the console’s firmware where the browser exposes it, and a desktop browser won’t offer an exploit launch. Read the exact firmware list and the linked upstream notes anyway. These are pinned, public project sources, not a promise that every route has been proven on every physical machine here. Exploits can hang or crash; use your own hardware, and don’t update firmware just to chase a card.
Pick your door: PS4 exploit archive · PS5 exploit archive · console-aware gateway.
No replies yet